Weekly Ransomware Intelligence Report, November 1, 2026
By ScruteXPublished
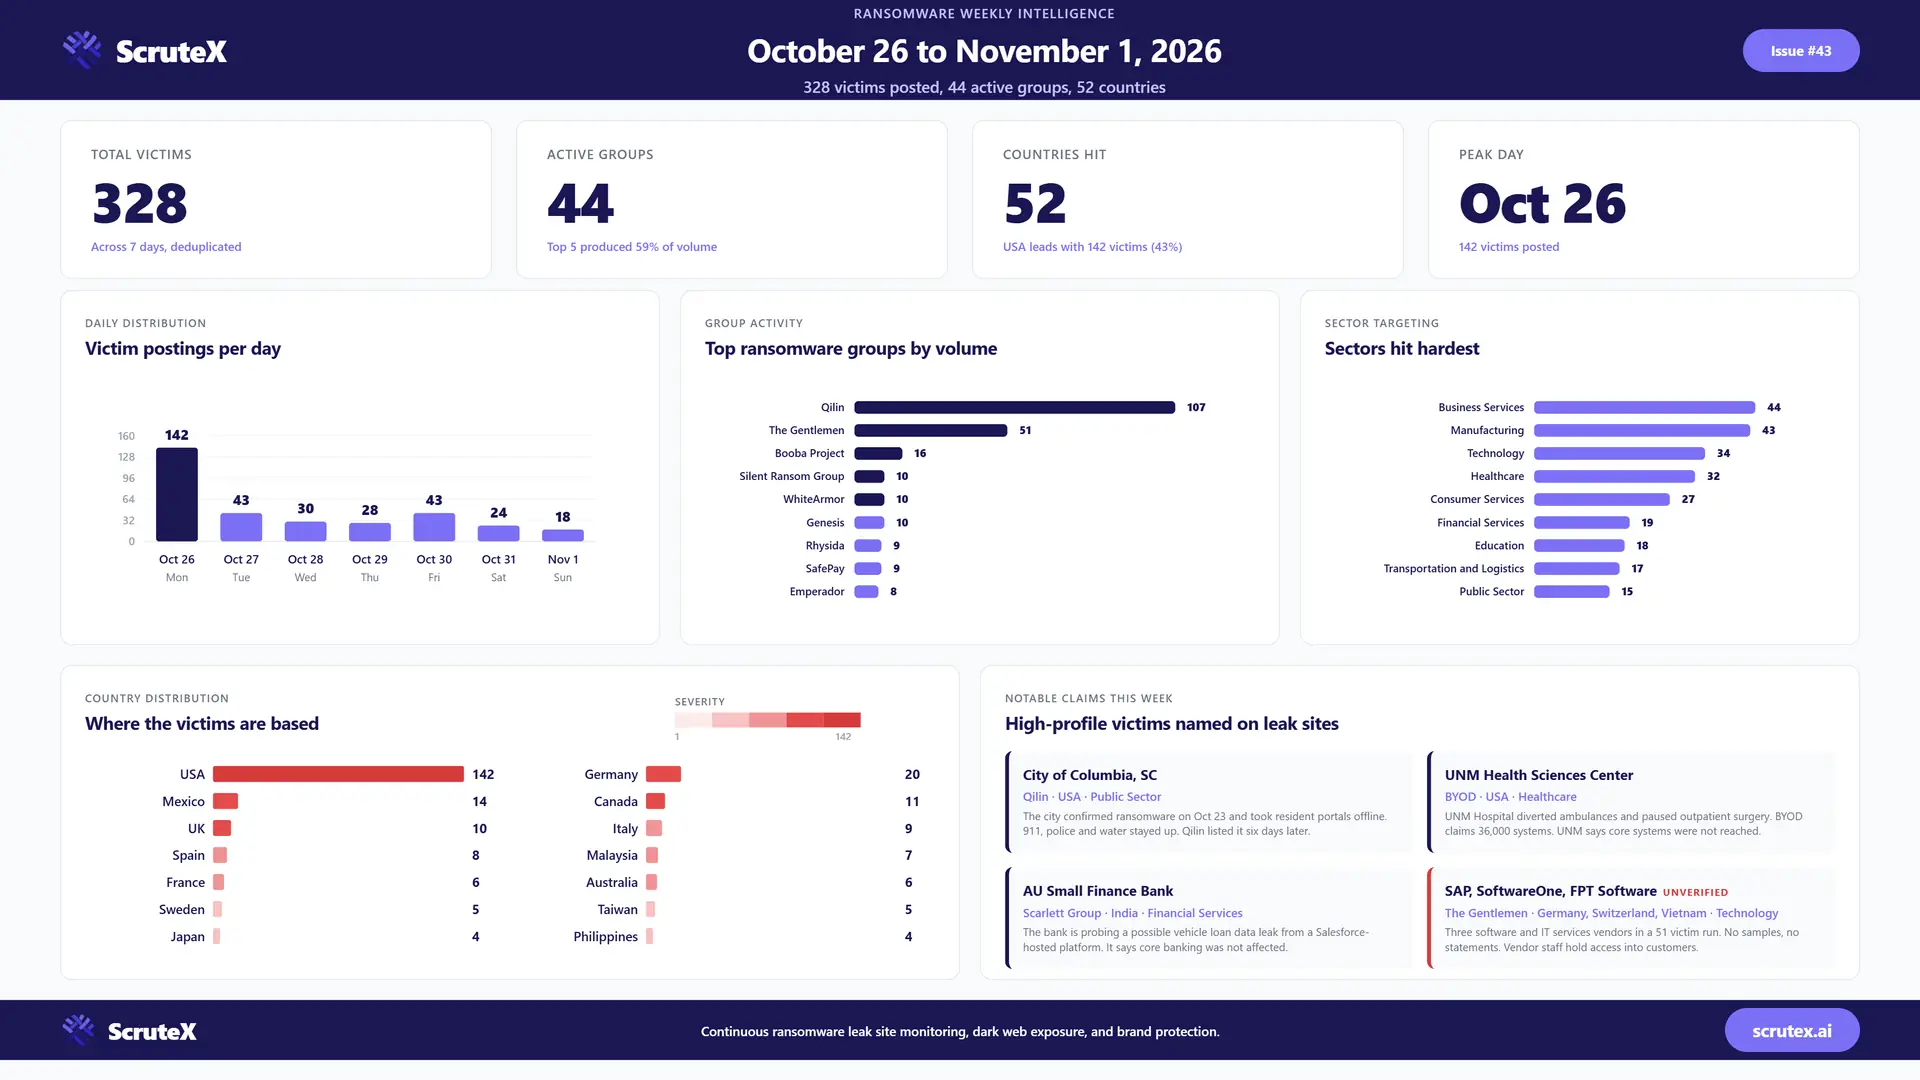
This is the Scrutex ransomware weekly for the October 26 to November 1, 2026 window. Our CTI team tracked 328 unique ransomware and extortion victim postings across 44 active groups and 52 countries. That is up 59% from 206 for October 19 to 25, and the highest weekly count in our recent issues.
Two groups explain almost all of the rise. Qilin posted 107 victims, up from 34, and The Gentlemen posted 51, up from 4. Take both out of both weeks and the rest of the leak site ecosystem posted 170 victims against 168 a week earlier. The broad level of activity did not change. Two operators published their backlogs.
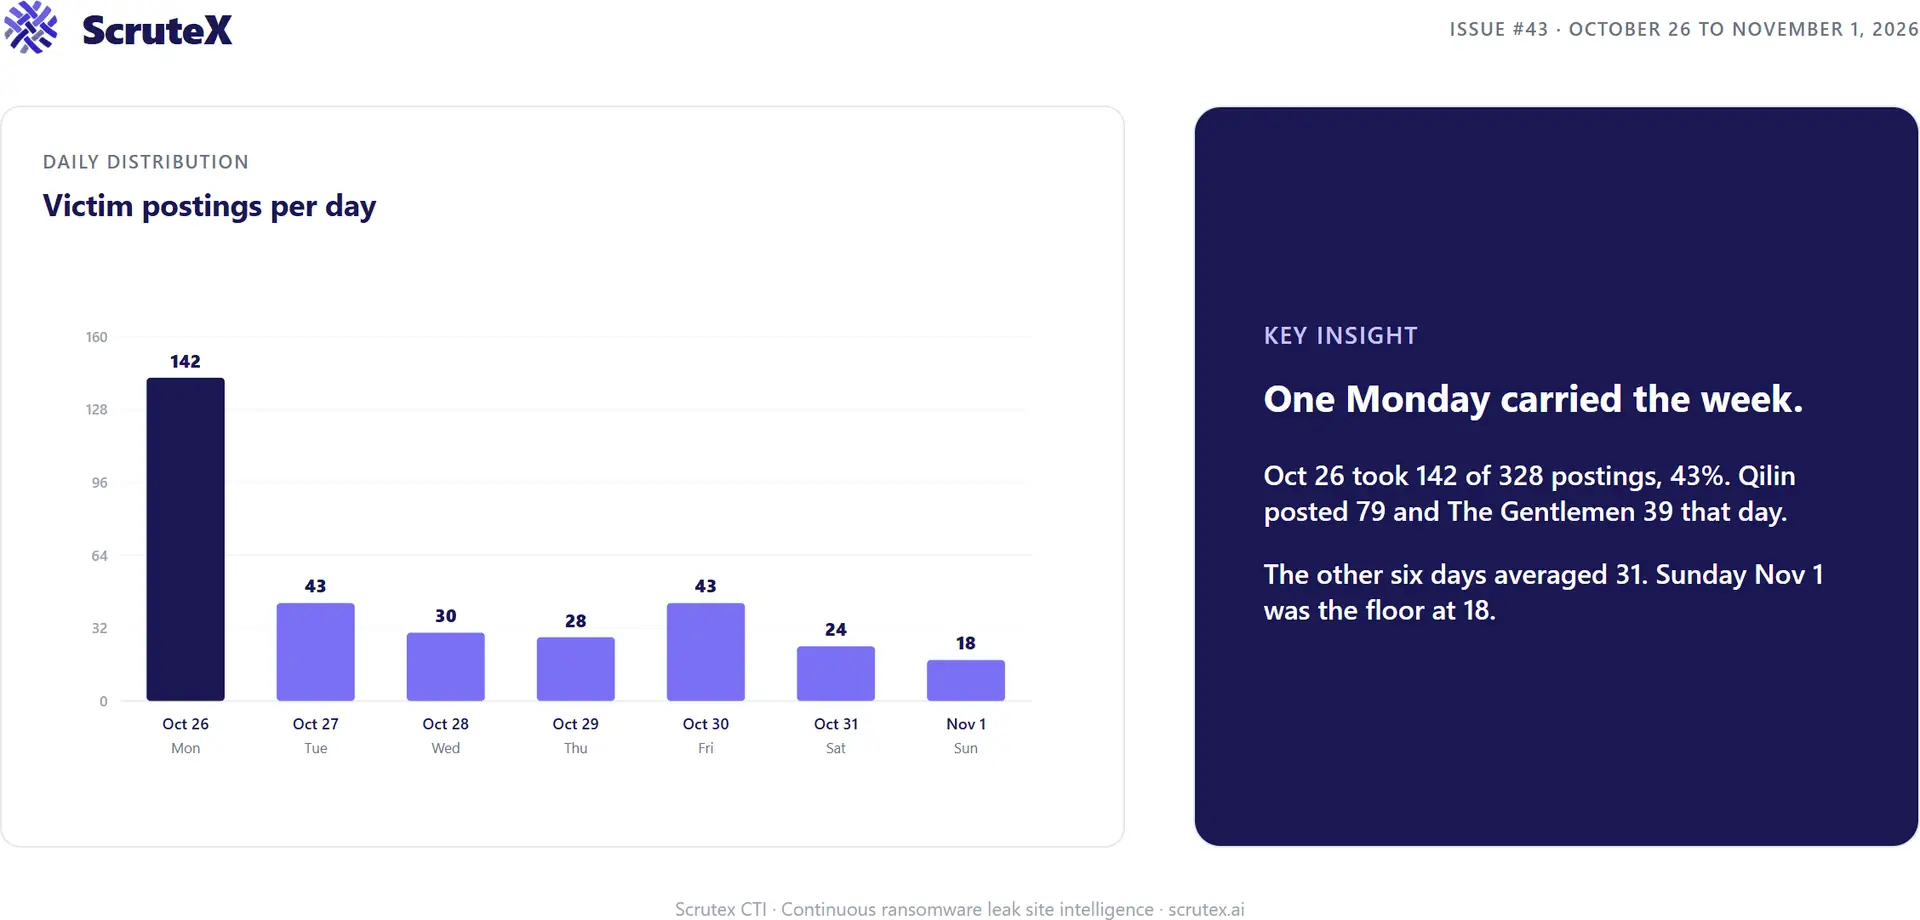
Most of that happened on one day. On Monday October 26, Qilin posted 79 victims and The Gentlemen 39, and the day closed at 142 postings, 43% of the week. These were not scrapes or re-reads. 51 of Qilin's 79 and 37 of The Gentlemen's 39 were carried by two or more independent trackers, and none had appeared in our previous two windows.
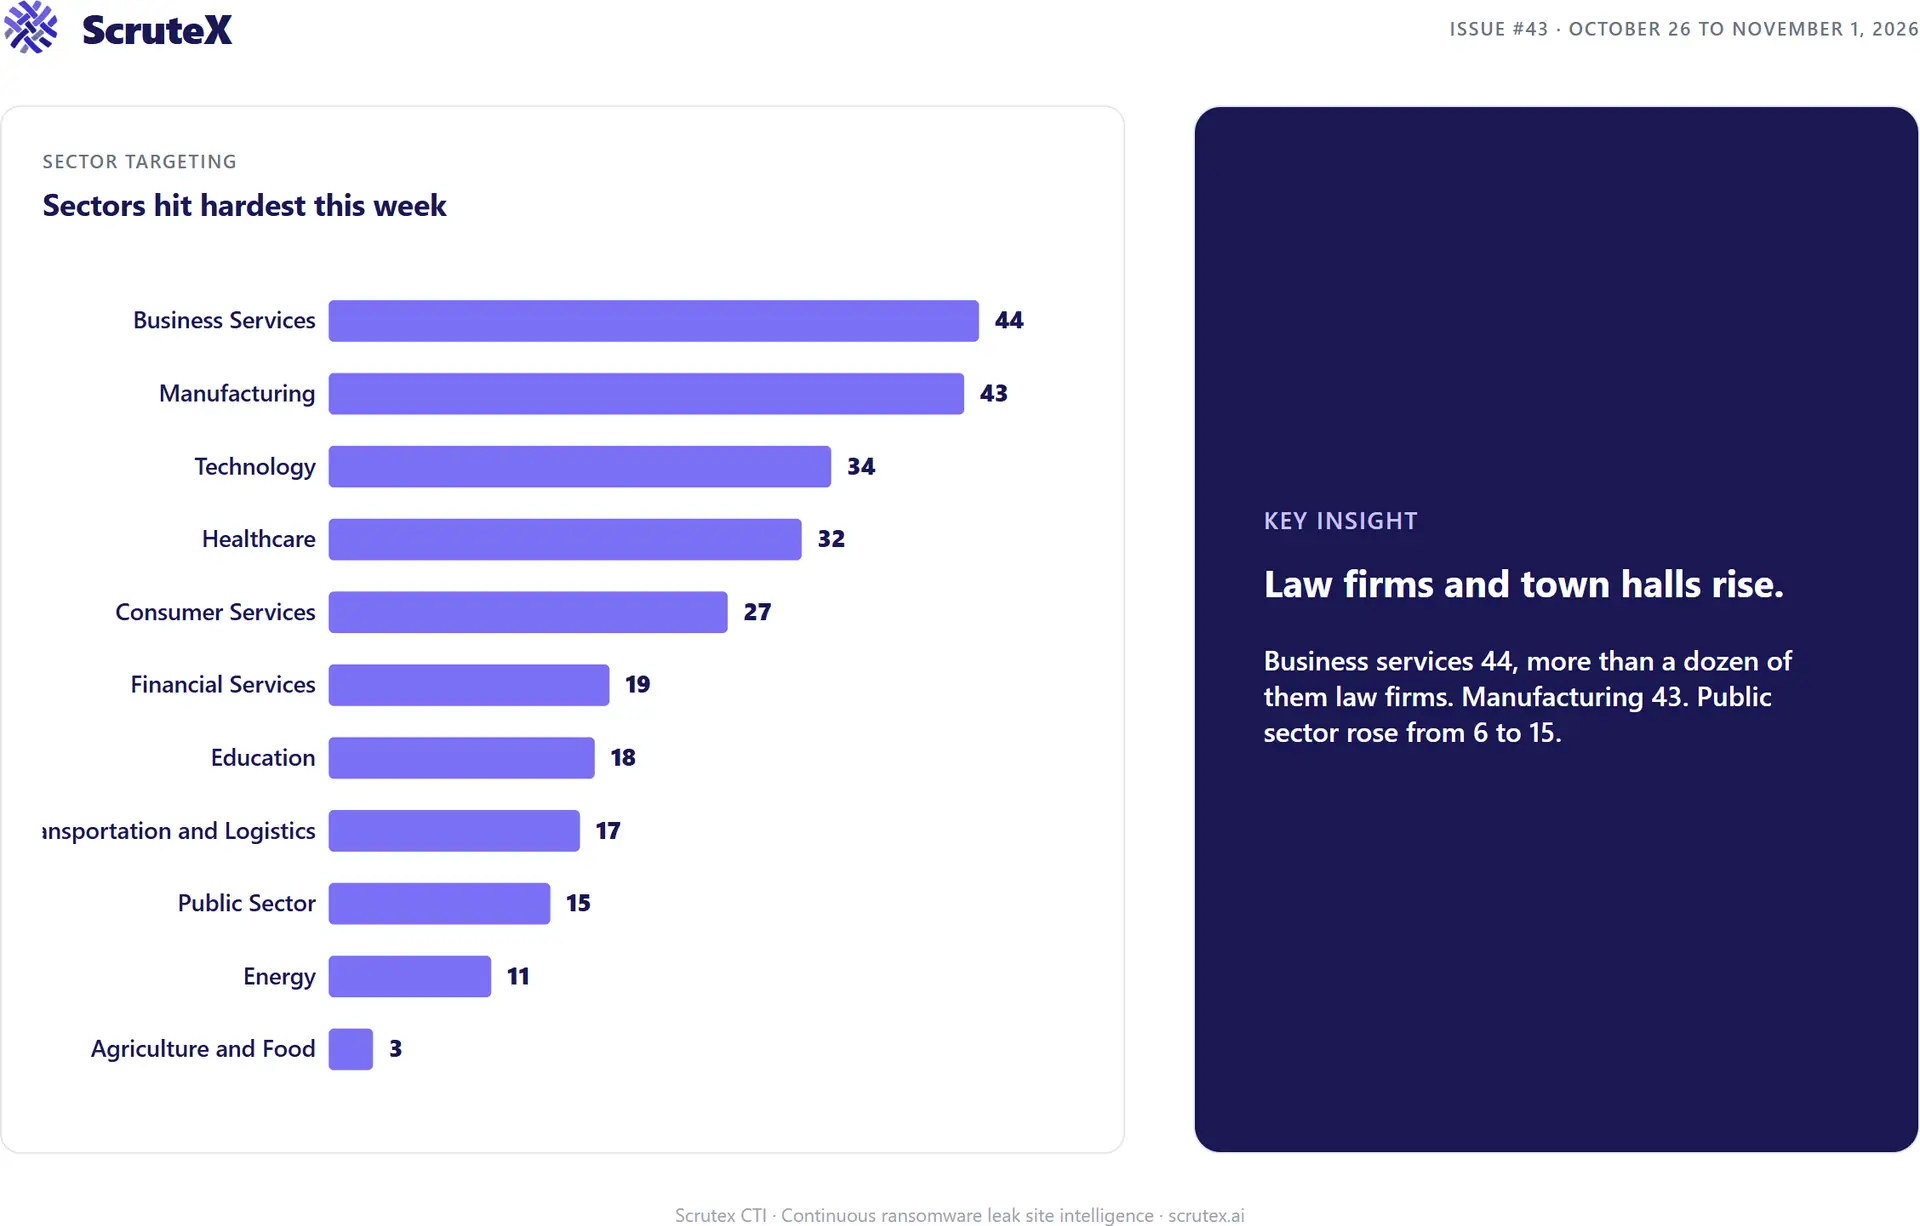
The United States took 142 postings, 43% of the week. Business services (44) and manufacturing (43) led the labelled sectors. Public sector rose from 6 to 15, and healthcare from 19 to 32.
Three of this week's postings match incidents the victims have already disclosed. The City of Columbia, South Carolina confirmed a ransomware attack on October 23, and Qilin listed it on October 29. The University of New Mexico Health Sciences Center diverted ambulances on October 26, and a group called BYOD claimed it the same day. AU Small Finance Bank in India said it is investigating a possible leak from a Salesforce-hosted platform after Scarlett Group posted it. A fourth, Svedala kommun in Sweden, confirmed a ransomware attack on October 1, and The Gentlemen listed it on October 28.
The rest of the week's large names are claims with no statement behind them: SAP, SoftwareOne and FPT Software (The Gentlemen), Ryder and KuCoin (WhiteArmor), Holcim (Emperador), Bristol City Council (WallStreet), and another six US law firms from Silent Ransom Group.
328 postings is more than most security teams can read. Finding the three that touch your own organisation or your suppliers is the actual job.
A note on how to read the numbers. Each count is a unique organisation named on a leak site during the window. We merge duplicate listings and mirrored sites, fold masked names into their later reveals, and leave out postings that do not name an organisation. Counts reflect leak site postings, not confirmed compromises, and by the time a victim is posted the intrusion is usually 30 to 90 days old.
This Week at a Glance
| Metric | Value |
|---|---|
| Total unique victims posted | 328 |
| Change on prior week | Up 59% (from 206) |
| Change excluding Qilin and The Gentlemen | Up 1% (168 to 170) |
| Active groups | 44 |
| Countries hit | 52 |
| Heaviest single day | Monday October 26 (142 posts, 43% of the week) |
| Quietest day | Sunday November 1 (18 posts) |
| Most targeted country | United States (142 victims, 43% of postings) |
| Most targeted sector | Business Services (44), then Manufacturing (43) |
| Top group by volume | Qilin (107, across 25 countries) |
| Confirmed incidents behind a listing | City of Columbia (SC), UNM Health Sciences Center, AU Small Finance Bank (investigating), Svedala kommun |
| Notable unverified claims | SAP, SoftwareOne, FPT Software, Vietnam Airlines, Ryder, KuCoin, Holcim, Bristol City Council, Morrison Foerster, Lowenstein Sandler |
Monday took 142 postings. The other six days ran 43, 30, 28, 45, 24 and 18, an average of 31 a day, which is close to last week's average of 29. Friday's 45 was the only other cluster, driven by Genesis posting nine US firms and Silent Ransom Group posting four law firms on October 30.
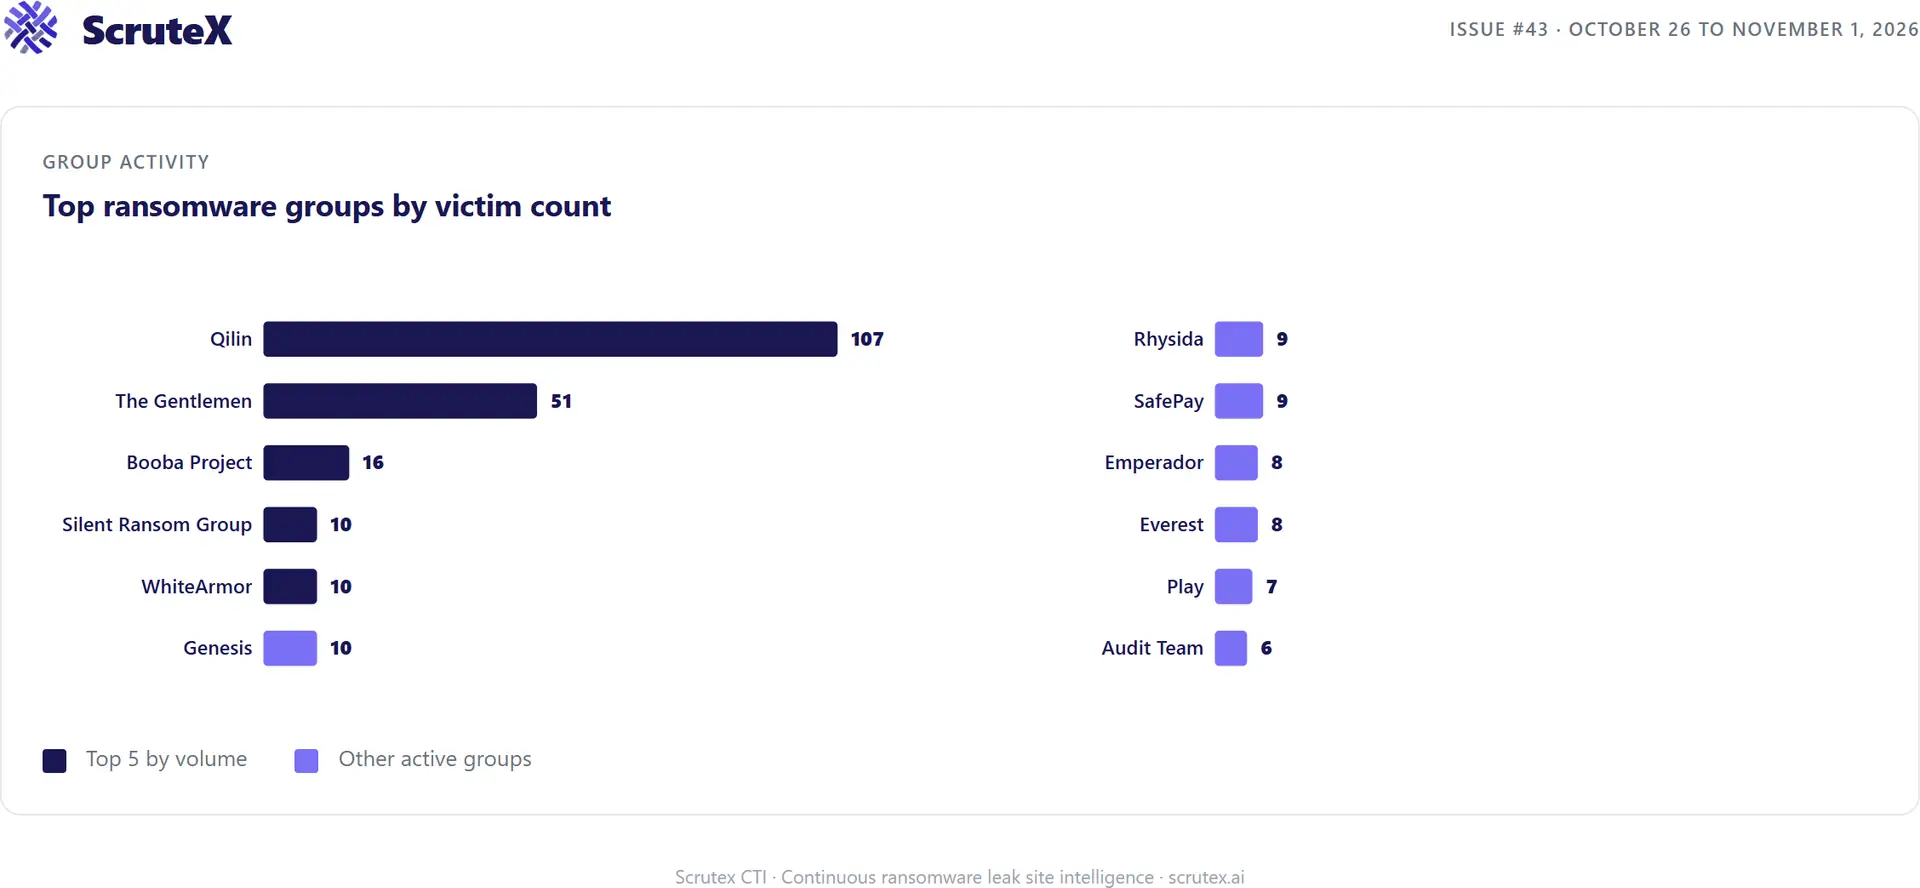
The top five groups took 194 of 328 postings, 59%, up from 42% last week. Below them, 26 groups posted three or fewer victims each, together accounting for 46.
The Monday Batch
A single day carrying 43% of a week can come from three places: a scraper reading a leak site's back catalogue for the first time, an operator republishing old victims, or an operator publishing new ones in bulk. Only the last one is new activity. We checked the first two.
It is not a scrape. In issue 41 one tracker re-read six leak sites in bulk and emitted 127 rows that no other tracker carried. This week's batch is different. 51 of Qilin's 79 Monday rows and 37 of The Gentlemen's 39 appeared on two or more of the five independent trackers in our pool, several on four or five, and Qilin's rows arrived in two publishing windows (about 00:00 and 12:00 UTC), which is how a leak site posts, not how a scraper backfills.
It is not a repost. None of the 158 victims the two groups posted this week appears in our October 12 to 18 or October 19 to 25 counts.
So it is a publishing decision. Qilin's weekly count had risen three weeks running before this one: 14, 23, 29, 34. Leak site posts trail the intrusion, often by one to three months, and an affiliate network as large as Qilin's tends to clear negotiations in waves. The Gentlemen ran a single midweek batch every week from early September and skipped it last week, posting only four. This week's 51 looks like two weeks of publishing arriving together.
What it means for defenders. Very little about October 26 itself. These intrusions happened weeks ago. What it does tell you is the scale of the two programmes. Qilin named victims in 25 countries this week, The Gentlemen in 20. If either group has been in your environment or a supplier's, the listing is the last step, not the first.
Group Activity Breakdown
| Rank | Group | Victims | Share | Last week | Notable Activity |
|---|---|---|---|---|---|
| 1 | Qilin | 107 | 33% | 34 | 79 on Oct 26 alone, posting on all seven days, 25 countries. City of Columbia (SC), Kaufman County (TX), Lodi Police Department, Saginaw Chippewa Indian Tribe, Burnaby school district, Proterial, JTEKT, Airbus SLC Mexico, Light Rail Manila, two US federal credit unions |
| 2 | The Gentlemen | 51 | 16% | 4 | 39 on Oct 26. SAP, SoftwareOne, FPT Software, Vietnam Airlines, Cherry Bekaert, SK Capital Partners, WABAG, Svedala kommun, France's Ined |
| 3 | Booba Project | 16 | 5% | 6 | Two drops, Oct 27 and Oct 29, every listing carried under two brand spellings. Four US local governments and a police department, three clinics |
| 4 | Silent Ransom Group | 10 | 3% | 9 | Morrison Foerster, Lowenstein Sandler, Susman Godfrey, ArentFox Schiff, Morrison Cohen, Moritt Hock, plus four masked names. Mirrored on LeakedData again |
| 5 | WhiteArmor | 10 | 3% | 4 | Ryder ($20 million demand), KuCoin, LoveSac, Echo.com. Posted on six of seven days |
| 6 | Genesis | 10 | 3% | 0 | Nine US professional services and construction firms on Oct 30 |
| 7 | Rhysida | 9 | 3% | 3 | MISC Group (Malaysia), INTI International University, a US charter school, two US financial services firms |
| 8 | SafePay | 9 | 3% | 0 | Nine bare domains on Oct 26, eight countries, including a Japanese university and a Taiwanese chipmaker |
| 9 | Emperador | 8 | 2% | 9 | Holcim, Afflelou, Uruguay's Punta Shopping, two Italian firms. No US victims |
| 10 | Everest | 8 | 2% | 6 | All on Oct 27. Natuzzi, a Singapore energy storage terminal, Canada's MediSolution |
| 11 | Play | 7 | 2% | 0 | All on Oct 27, six of them US |
Also active: Audit Team, Aurora and Akira (6 each), Payload, Everstake and Interlock (5 each), Settra (4), and a long tail of DragonForce, N0n, Shiba, DireWolf, WallStreet, LockBit, Scarlett Group, Crypto24, PayoutsKing, Pear, Barracuda, Global Secret Group, Vexy, BYOD, Falcon, LeakNet, Anubis, Panzer, KryBit, Syntax, Doommageddon, INC Ransom, RansomHouse, NightSpire, Sarcoma and HYFLOCK, each with one to three listings.
Four observations:
Qilin is now a third of the ecosystem. 107 listings in a week, posting every day, in 25 countries, 48 of them in the US. Its victim list reads like a cross-section of the mid market with a public sector edge: a South Carolina state capital, a Texas county, a California police department, a federally recognised tribe, a Canadian school district, an Australian council and a Hawaii state energy research authority, alongside Japanese industrial names (Proterial, formerly Hitachi Metals, and a JTEKT entity), an Airbus site in Mexico and Light Rail Manila. 13 of its 107 were bare domains with no other detail. Unit 42 confirmed on October 19 that Qilin affiliates are still exploiting the PAN-OS GlobalProtect flaw CVE-2026-0257. More in the CVE section.
The Gentlemen's batch came back, twice over. It skipped its usual midweek drop last week and posted four. This week it posted 51, three quarters of them on Monday. The list is heavy on IT and software vendors (SAP, SoftwareOne, FPT Software, Northwest Micro Systems, SuperScale) and on professional services (Cherry Bekaert, one of the largest US accounting firms, and the private equity firm SK Capital Partners). A vendor or an auditor on a leak site matters less for its own data than for the access its staff hold into its customers.
N0n fell from 26 to 3. Its numbered "Company #" slots continued, and we do not count them. After two weeks at the top of the chart, the crew posted almost nothing under a name.
Five of the top eleven are back from zero. Genesis, SafePay and Play posted nothing last week, and Rhysida and Booba Project were well below this week's level. All five published in one or two drops. Leak sites post when negotiations close, not when intrusions happen, and that churn is the normal rhythm.
New and Returning Groups
Genesis. Nine US victims on October 30 and one on October 27: four professional services firms, a crane and construction contractor, an engineering firm, an investment group, a work injury clinic and a Canadian psychometrics publisher. The profile is small and mid-sized US businesses with thin security teams.
SafePay. Nine bare domains on one afternoon, spread across Taiwan, Japan, Argentina, Israel, Mexico, Ecuador, Peru and the US. Two are universities (jumonji-u.ac.jp in Japan and Mexico's Universidad Autonoma de Aguascalientes) and one is a Taiwanese semiconductor firm. SafePay publishes domains with no description, so each listing tells you who and nothing about what.
Scarlett Group. Three listings, and one of them has a public response. AU Small Finance Bank, one of India's largest small finance banks, said on October 30 that it is investigating a possible leak of vehicle loan customer data, centred on a Salesforce-hosted platform holding limited information, and that its core systems are unaffected. The group claims KYC records, PAN and Aadhaar numbers and loan files. Its other two listings are sunnybrook.ca, the Toronto hospital network, which a different group (0apt) claimed in February, and the US retailer Spencer's.
BYOD. One victim, and the week's most disruptive incident: the University of New Mexico Health Sciences Center. Covered below. BYOD's first listings in September were reposts of another crew's victims, and its claim of 36,000 compromised systems should be read with that history in mind.
Booba Project, broadening. Sixteen listings in two drops. Its earlier targets were law firms, architects and insurers. This week it posted Big Spring (TX), South Weber City (UT), Terrebonne Parish Government (LA), the Charter Township of Commerce (MI) and the Circleville Police Department (OH), plus the California School Boards Association, a credit trade association and three medical practices. Public reporting links the group's initial access to infostealer logs bought from underground markets. Small local governments are exactly where a reused staff password goes unnoticed.
Sector Targeting Analysis
| Rank | Sector | Victims | Share of labelled | Last week |
|---|---|---|---|---|
| 1 | Business Services | 44 | 16% | 28 |
| 2 | Manufacturing | 43 | 16% | 31 |
| 3 | Technology | 34 | 13% | 19 |
| 4 | Healthcare | 32 | 12% | 19 |
| 5 | Consumer Services | 27 | 10% | 15 |
| 6 | Financial Services | 19 | 7% | 6 |
| 7 | Education | 18 | 7% | 7 |
| 8 | Transportation and Logistics | 17 | 6% | 6 |
| 9 | Public Sector | 15 | 6% | 6 |
| 10 | Energy | 11 | 4% | 4 |
| 11 | Agriculture and Food | 3 | 1% | 5 |
| 12 | Hospitality and Tourism | 3 | 1% | 5 |
60 of 328 postings carried no sector label and are excluded from the share column. Almost every sector rose with the total. The shifts in share are what matter.
Business services is the law firm story for the second week. 44 postings, and at least 13 of them are law firms. Silent Ransom Group named six large US firms. Beyond that crew: Beasley Allen (Falcon), Phillips Nizer (RansomHouse), Becker & Poliakoff (Syntax), Noelker and Hull (Rhysida), a Chicago practice (INC Ransom), and Smith Feddeler & Smith and Meshbesher & Spence (Qilin). Qilin also listed Miller Stratvert, a New Mexico firm that arrived without a sector. Two accounting firms, Cherry Bekaert and Alten Sakai, sit alongside them. Twenty-six law firms in two weeks is a campaign pattern, not noise.
Public sector more than doubled, from 6 to 15, and it is local. Qilin took the City of Columbia, Kaufman County, the Lodi Police Department, the Saginaw Chippewa Indian Tribe and Fairfield City Council in New South Wales. Booba Project took four US towns and a police department. The Gentlemen listed Svedala kommun in Sweden and France's national demographic research institute, Ined. WallStreet listed Bristol City Council and Payload a German state development company. Local government runs 911 dispatch, utilities billing and resident records on budgets that rarely include a security team.
Healthcare rose to 32 from 19. UNM Health is the headline. The rest is the familiar small practice pattern: retina, rheumatology, orthopaedic, dental, radiology and eye surgery practices, a nursing and rehabilitation centre, a rural Nebraska hospital, a sleep lab and Oregon's Santiam Hospital. One leak post this week was titled to advertise patients' Social Security numbers, a tactic aimed at the patients, not the provider.
Financial services tripled, from 6 to 19. Three US credit unions, one of them serving Hawaii law enforcement (Qilin), AU Small Finance Bank, a Thai capital firm (LockBit), a Bolivian investment house (The Gentlemen), insurance agencies in Canada, claims processors in the US. Large banks stay off leak sites. Their claims processors, credit unions and SaaS platforms do not.
Energy rose to 11. Two US electric cooperatives or power associations (Delta Electric Power Association in Mississippi, listed by Qilin, and Inside Passage Electric Cooperative in Alaska, listed by DragonForce), a US oil and gas producer (Akira), Malaysia's MISC Group (Rhysida), a Singapore energy storage terminal (Everest) and India's WABAG, a water treatment engineering group (The Gentlemen).
Country Distribution
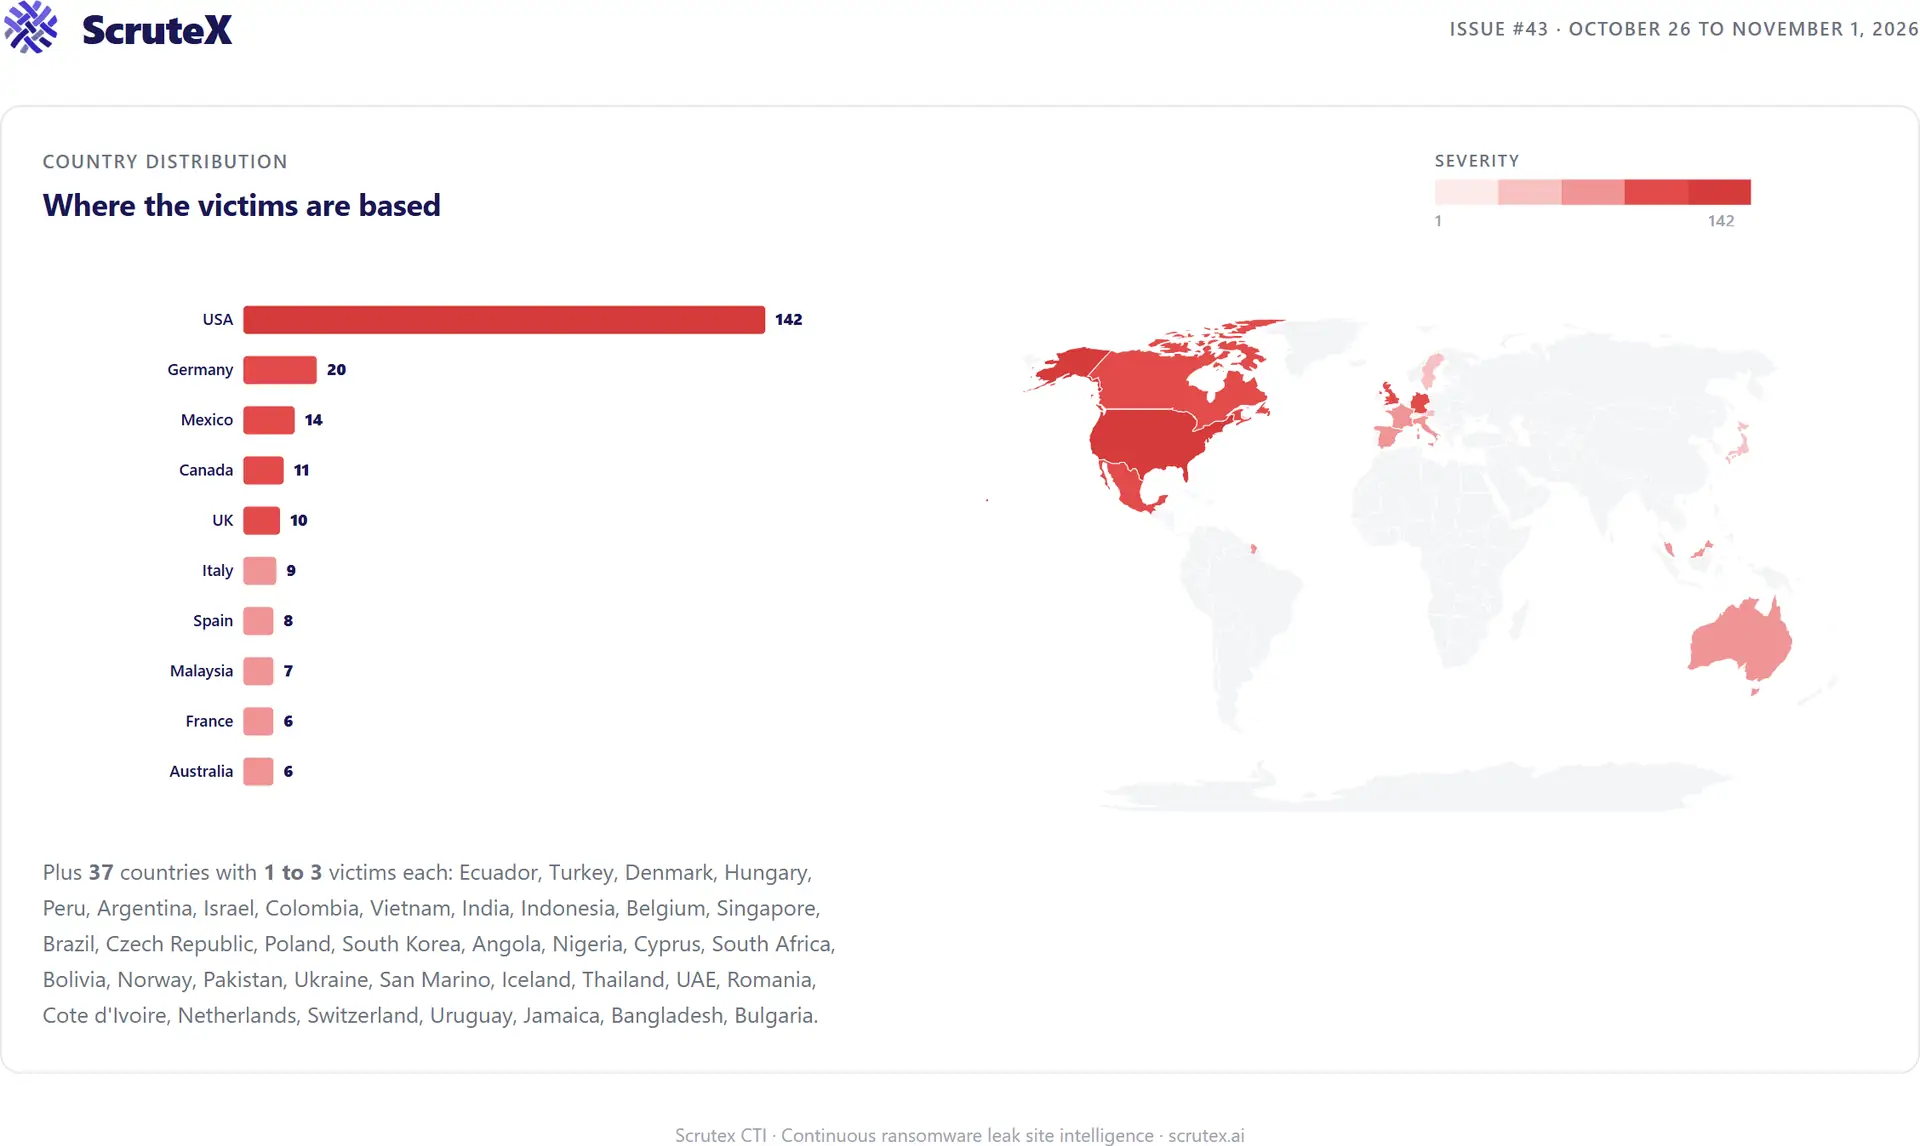
| Rank | Country | Victims | Share | Last week |
|---|---|---|---|---|
| 1 | United States | 142 | 43% | 89 |
| 2 | Germany | 20 | 6% | 21 |
| 3 | Mexico | 14 | 4% | 4 |
| 4 | Canada | 11 | 3% | 4 |
| 5 | United Kingdom | 10 | 3% | 6 |
| 6 | Italy | 9 | 3% | 4 |
| 7 | Spain | 8 | 2% | 5 |
| 8 | Malaysia | 7 | 2% | 3 |
| 9 | France | 6 | 2% | 4 |
| 10 | Australia | 6 | 2% | 3 |
A further 42 countries carried one to five postings each, among them Sweden, Taiwan, Japan, the Philippines, Austria, Ecuador, Turkey, Denmark, Hungary, Peru, Argentina, Israel, Colombia, Vietnam, India, Indonesia, Belgium, Singapore, Brazil, Angola, Nigeria, South Africa, Bolivia, Pakistan, Ukraine, Thailand, the UAE, Romania, Côte d'Ivoire, Switzerland, Uruguay, Jamaica, Bangladesh and Bulgaria. 23 postings carried no country.
The US share held at 43%. The count rose by 53, almost all of it Qilin (48 US victims) and The Gentlemen (16).
Germany held steady at 20 across seven crews, the second week running at that level. Qilin posted nine German victims, mostly industrial and professional services, and The Gentlemen four. Payload added a state development company and an education provider.
Mexico more than tripled, from 4 to 14. Qilin posted seven Mexican victims, including a steel group and an Airbus site, The Gentlemen two, and Rhysida, SafePay, DireWolf, Emperador and LockBit one each. Mexico's manufacturing base supplies US automotive and aerospace programmes, so a Mexican plant on a leak site can be a US supply chain incident.
Malaysia reached 7 from four crews: a toll road operator, a parking platform and a listed technology group (Qilin), MISC Group and INTI International University (Rhysida), a hospital group (Crypto24) and a technology firm (N0n).
Notable Claims and Incidents
Every entry below is a claim the actor posted. We say where the organisation or an authority has said something, and rate how far the claim itself can be trusted.
Incidents the victims have disclosed
Qilin lists the City of Columbia, South Carolina. Posted October 29. The city confirmed on October 23 that a ransomware attack had disrupted online services, including its resident portal MyColaSC, online animal services, park reservations and GIS. Police, fire, 911 and Columbia Water stayed up. SLED is investigating and the city has not said whether data was taken. Confidence: High that the city suffered a ransomware incident. Medium that Qilin is responsible, because the listing followed the disclosure and the city has not named a group.
BYOD lists the University of New Mexico Health Sciences Center. Posted October 26, then again as an "UPDATE" on October 27. UNM Health reported a cyber incident on October 26 that caused system outages: it limited new admissions, diverted ambulances and postponed outpatient surgeries. Critical systems were back early on October 27, and the university said the attackers did not penetrate core systems or servers. BYOD claims 36,000 systems. Confidence: High that an incident occurred. Low on BYOD's scale claim. The university has not attributed the attack or called it ransomware.
Scarlett Group lists AU Small Finance Bank. Posted October 29. The bank said on October 30 that it is investigating a possible leak involving vehicle loan customers, focused on a Salesforce-hosted platform, and that its core banking systems are not affected. Confidence: Medium. The bank has confirmed an investigation, not a breach, and has not confirmed that the platform is the source of the data the group holds. If you are a vehicle loan customer, expect targeted phishing that quotes your loan details.
The Gentlemen lists Svedala kommun. Posted October 28. The Skåne municipality shut down its digital systems on October 1 after a ransomware attack and has since said information was, with high probability, lost or leaked. Confidence: Medium that The Gentlemen is the group. Early reporting said no group had claimed the attack, and this listing is the first claim we have seen.
Claims with no public response
The Gentlemen lists SAP, SoftwareOne and FPT Software. SAP and SoftwareOne on October 26, FPT Software on October 27. No volume, no samples and no statements from any of the three. One public tracker rates the SAP listing at 70% confidence. Confidence: Low on each. The Gentlemen has filed subsidiaries and resellers under parent brand names before. For customers, the useful question is not whether the vendor lost data. It is whether the vendor's support or delivery staff hold standing access to your environment, and how you would cut it.
The Gentlemen lists Vietnam Airlines. Posted October 26. The airline disclosed a 2025 breach through its Salesforce account and was listed by Qilin in January 2026. Confidence: Low. Recycled data from an earlier incident is a common way to fill a listing.
Silent Ransom Group lists six more law firms. Morrison Foerster, Lowenstein Sandler, Susman Godfrey, ArentFox Schiff, Morrison Cohen and Moritt Hock & Hamroff, between October 26 and 30, mirrored on LeakedData. Two of its masked entries were revealed as ArentFox and Moritt Hock on the same day, and four remain masked. Confidence: Medium that the group has active access into the legal sector, given its documented method and the FBI's warnings. Low on each firm. None has commented.
WhiteArmor lists Ryder and KuCoin. Ryder on October 27 with a reported $20 million Bitcoin demand, KuCoin the same day. WhiteArmor opened last week with J.B. Hunt, Whirlpool and Hisense, and continues with large logistics and consumer names. It also listed its own Telegram channel and a "Verification" page as victims, which we excluded. Confidence: Low. Neither company has commented.
Emperador lists Holcim. Posted October 31. Emperador listed AB InBev last week with a $1 million demand and a data description that read like the contents of a marketing tool. Confidence: Low. Holcim has not commented.
WallStreet lists Bristol City Council. Posted October 27, with no data volume. The council has previously warned about risk from delayed IT updates. Confidence: Low. No council statement.
Low signal claims this week. 37 postings are a bare domain and 18 are masked to a few characters, so 273 of 328, 83%, name an organisation in words, the same share as last week. Qilin (13), SafePay (8) and Settra (4) account for most of the bare domains. Audit Team, Everstake and PayoutsKing account for most of the masked entries.
Updates on last week's claims. None of last week's law firms, PwC, OpenText, AVEVA, J.B. Hunt, Whirlpool, Hisense or AB InBev has published anything further that we have found.
Top CVEs These Groups Are Exploiting
The table covers this week's active groups where a named source supports the attribution. Scores are the published base scores.
| CVE | Product | CVSS | Who is using it | Why it matters |
|---|---|---|---|---|
| CVE-2026-0257 | Palo Alto Networks PAN-OS GlobalProtect, authentication bypass | 7.8 reported by The Hacker News, 9.1 in other sources | Qilin, INC Ransom, Settra | Unit 42's October 19 to 20 updates name Qilin and INC. Arctic Wolf assesses Qilin intrusions through it are likely ongoing. Patched May 13, on CISA KEV. Qilin posted 107 this week |
| CVE-2023-27532 | Veeam Backup and Replication, credential exposure | 7.5 | Qilin and INC (per Unit 42), The Gentlemen (per Group-IB) | Chained after the VPN access. The backup server holds credentials to the rest of the estate |
| CVE-2024-55591 | Fortinet FortiOS and FortiProxy, authentication bypass | 9.8 | The Gentlemen | Group-IB names it the group's primary access route, alongside VPN credentials without MFA |
| CVE-2024-40766 | SonicWall SonicOS SSLVPN, improper access control | 9.8 | Akira | Sustained Akira activity tied to it by Arctic Wolf, Rapid7 and CISA |
This week's KEV additions. CISA added Cisco Secure Firewall ASA and FTD CVE-2026-76418 on October 29, alongside a GitLab flaw, with a three-day federal deadline of November 1.
| CVE | Product | Added | What to know |
|---|---|---|---|
| CVE-2026-76418 | Cisco Secure Firewall ASA and FTD, Remote Access SSL VPN denial of service | Oct 29 | CVSS 8.6. Unauthenticated, remote, reloads the firewall. Exposure needs the SSL VPN enabled and secondary authentication on a tunnel group. Cisco confirms exploitation. No public IOCs yet. Not flagged for ransomware use, but a VPN that reloads on demand is a VPN that drops its logs and sessions on demand |
The headline is the same as last week. The two biggest publishers this week have documented edge-device access routes: Qilin on PAN-OS, The Gentlemen on FortiOS and VPN credentials without MFA. The groups behind most of the named law firms, Silent Ransom Group and Falcon, use phone calls, not CVEs. Both routes were open this week.
Attribution accuracy note. We list a group against a CVE only where a named source supports it. The Gentlemen's Fortinet and Veeam links and Akira's SonicWall link are carried forward from published research and were not re-observed this week.
Infrastructure and Operational Shifts
Batch publishing is becoming the norm for the largest groups. 118 postings from two groups in one day. Qilin's 79 arrived in two publishing windows about twelve hours apart. A defender who checks leak sites on a weekly cycle sees the same data as one who checks hourly, but a supplier listed on a Monday can be in the news before your procurement team has opened its inbox.
Masked names, revealed the same day. Silent Ransom Group posted "A... F..." and "M... H..." on October 30 and named ArentFox Schiff and Moritt Hock & Hamroff the same day. Four masked entries remain, including a single "L..." posted the day it named Lowenstein Sandler. For counting, we merge a masked entry only when its initials match a reveal from the same day. For a defender, initials that match your firm's name are an incident on the day they appear.
Two brand names, one crew. Booba Project posted every one of its sixteen victims under two spellings ("Booba Project" and "booba team"). Silent Ransom Group mirrored its list on LeakedData again. We count each organisation once. Counted naively, these two crews alone would add 26 to the week.
Site furniture and test entries. WhiteArmor listed its own Telegram channel and a "Verification" tile as victims. ULose posted two test entries ("zzq-test" and a probe string). LeakNet posted a headline advertising patients' Social Security numbers with no organisation named. Everstake masked each of four domains twice, once per tracker, with different numbers of stars. All of these are excluded or merged.
Key Takeaways for Defenders
Hunt for Qilin's access route if you run GlobalProtect. Qilin posted 107 victims this week and Unit 42 confirms its affiliates are still using CVE-2026-0257 five months after the patch. Check for VPN sessions you cannot explain, changes to ESXi
execInstalledOnly, access to domain controller VMDK files and Veeam CVE-2023-27532 exposure. Rotate any credential that passed through the gateway while it was unpatched.Patch Cisco ASA and FTD this week. CVE-2026-76418 is exploited and the federal deadline has already passed. If you run Remote Access SSL VPN with secondary authentication, you are in scope.
Ask your law firms the help desk question again. Twenty-six law firms in two weeks, most of them listed by crews that get in by phone. Ask outside counsel in writing how they verify IT support calls, and whether anyone has contacted them claiming to hold your matter files.
Review vendor access for the software houses on this week's list. If SAP, SoftwareOne, FPT Software or any other listed IT provider holds standing remote access, partner accounts or delegated admin rights in your environment, confirm what it is, who uses it and how quickly you could revoke it. Do this before the vendor confirms anything.
Local governments: assume infostealer credentials are in play. Booba Project buys stealer logs. Qilin hit a state capital, a county and a police department. Reset passwords for any staff account found in a stealer log, enforce MFA on every remote access path, and know who answers the phone at 2 a.m. when the resident portal goes down.
Most of that is triage before it is defence. Somebody has to read 328 postings, set aside the mirrors, the masked duplicates and the test entries, and work out which of the rest touch your organisation or your suppliers.
Where Scrutex Fits
Scrutex Threat Insights monitors ransomware leak sites and dark web sources continuously and matches what it finds against your own domains and your named suppliers, so a listing that names your organisation, your outside counsel or a software vendor reaches you as an alert and not as a line in a weekly roundup. Data Exposure Insights watches for employee credentials in infostealer logs and breach corpora, the raw material crews like Booba Project buy. Vulnerability Insights prioritises flaws like CVE-2026-0257 and CVE-2026-76418 by real-world exploitation against your exposed assets, not by raw CVSS. None of them can tell you whether a claim is true. All of them can tell you, quickly, whether it is about you.
Start at scrutex.ai/signup or read more at scrutex.ai/solution/threat.
Frequently Asked Questions
How many ransomware attacks were there in the week of October 26 to November 1, 2026?
Scrutex tracked 328 unique victim postings across 44 active groups and 52 countries. That is up 59% from 206 the week before, almost entirely because Qilin and The Gentlemen published large batches. Without those two groups, the count was flat at 170 against 168. These are leak site postings, not confirmed compromises, and the intrusion is usually 30 to 90 days older than the posting.
Which ransomware group was most active?
Qilin, with 107 listings across 25 countries, a third of the week. The Gentlemen was second with 51, then Booba Project with 16. Qilin's weekly count has now risen four weeks running: 14, 23, 29, 34 and 107.
Was SAP hit by ransomware?
The Gentlemen listed SAP on October 26 with no data volume, no samples and no description of what was taken. SAP has not commented and we found no independent reporting. We rate the claim low confidence.
Did the City of Columbia, South Carolina suffer a ransomware attack?
Yes. The city confirmed a ransomware attack on October 23 that took several online services offline, while police, fire, 911 and water kept running. Qilin listed the city on October 29. The city has not named the group or said whether data was taken.
What happened at UNM Health?
The University of New Mexico Health Sciences Center reported a cyber incident on October 26 that caused outages, ambulance diversions and postponed surgeries. Critical systems were restored early on October 27. A group called BYOD claims to have compromised 36,000 systems. The university says the attackers did not reach core systems and has not called the incident ransomware.
Was AU Small Finance Bank breached?
AU Small Finance Bank is investigating a possible leak of vehicle loan customer data from a Salesforce-hosted platform after Scarlett Group posted a claim. The bank says its core systems are not affected and has not confirmed a breach.
Why are law firms being targeted?
At least thirteen law firms were named this week, after thirteen last week. Silent Ransom Group and similar crews get in by calling staff while posing as IT support, not by exploiting software. Law firms hold their clients' most sensitive documents, which gives an extortion crew a hold over the firm and its clients at once.
Which CVEs should I patch this week?
PAN-OS GlobalProtect CVE-2026-0257, which Qilin and INC are still exploiting, and Veeam CVE-2023-27532, which they chain after it. Cisco ASA and FTD CVE-2026-76418 was added to CISA's KEV catalogue on October 29 with a November 1 deadline.
Where can I get this in real time instead of weekly?
Scrutex Threat Insights monitors leak sites and dark web sources continuously and matches findings against your own domains and your named suppliers, so a relevant listing reaches you when it is posted, not in the following Monday's roundup.